
Sure, you can handle it. But should you?
Let our experts manage the tech maintenance while you focus on your business.
Let our experts manage the tech maintenance while you focus on your business.
Release Notes for Mindbreeze InSpire
Version 26.7
Release Highlights
Mindbreeze InSpire as an agentic tool
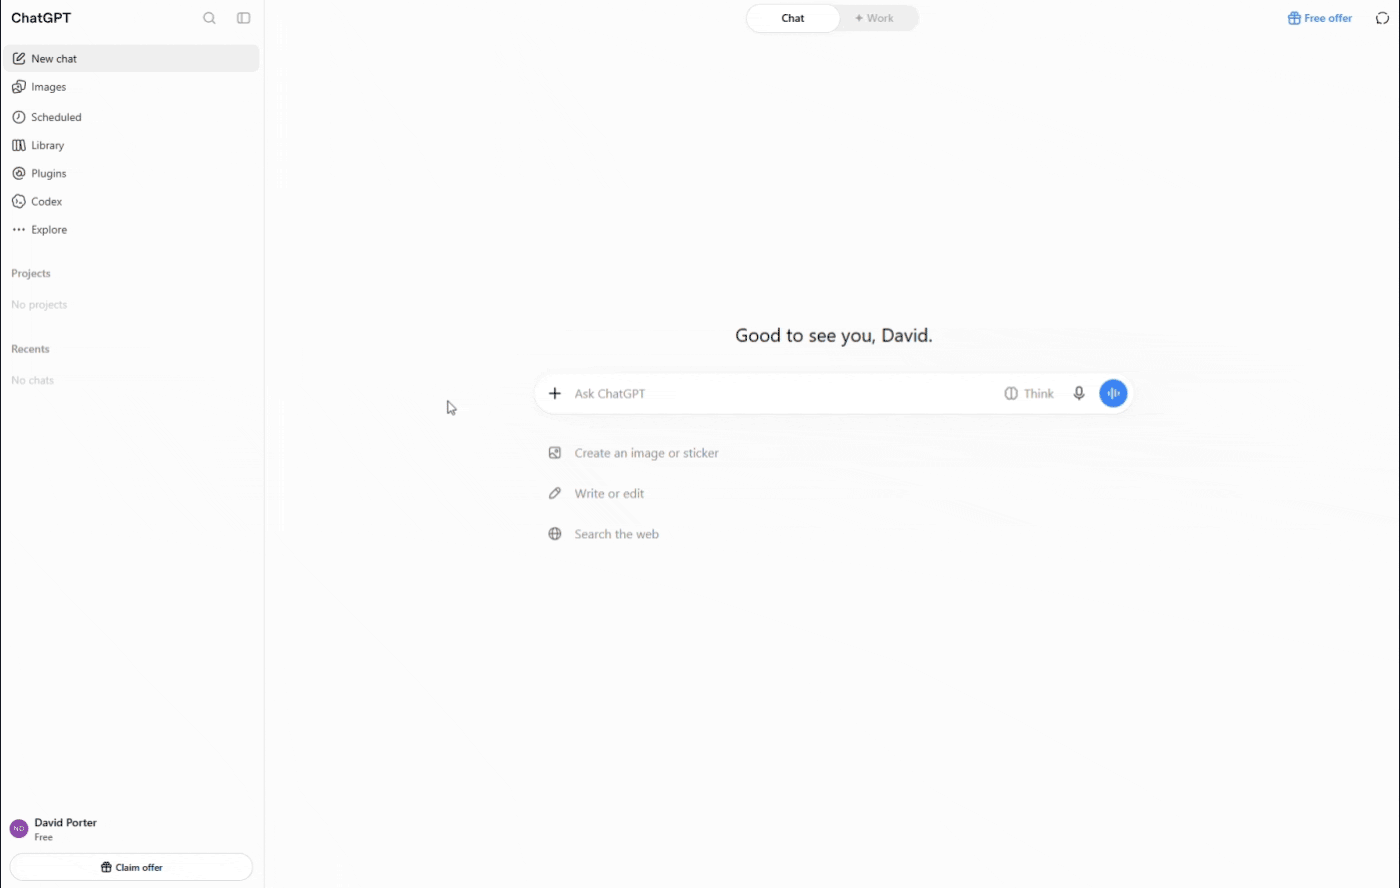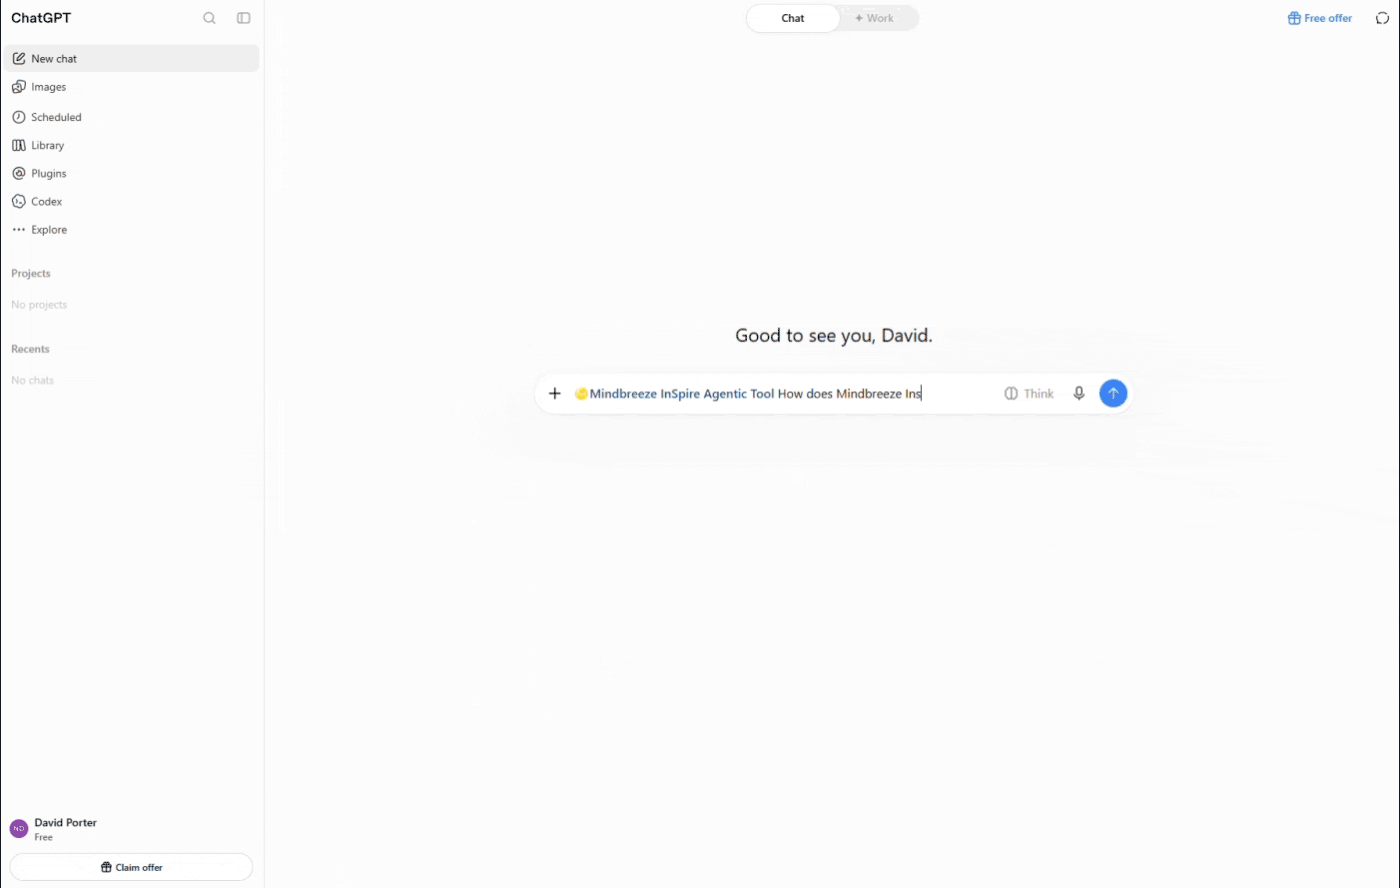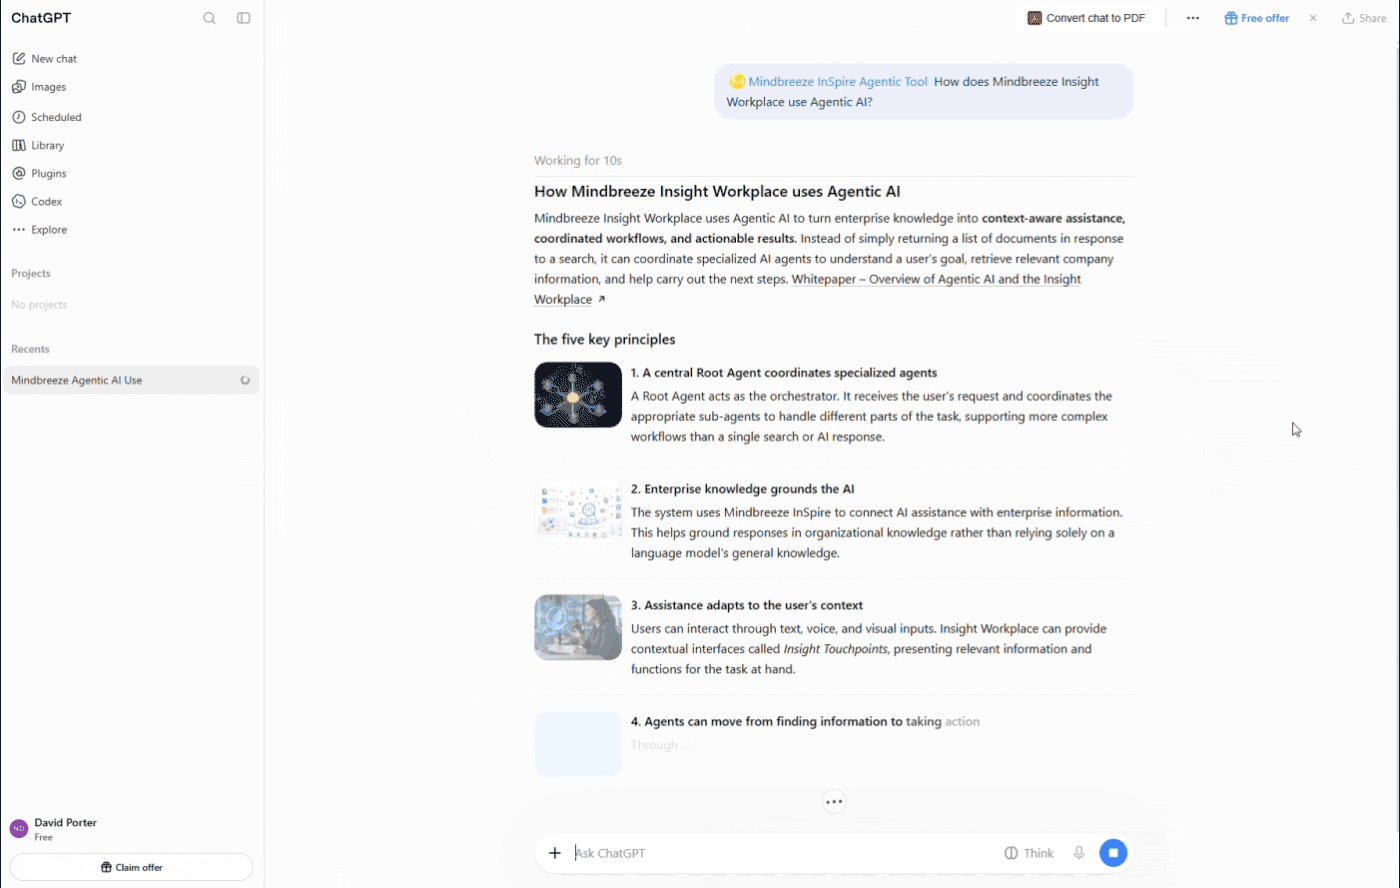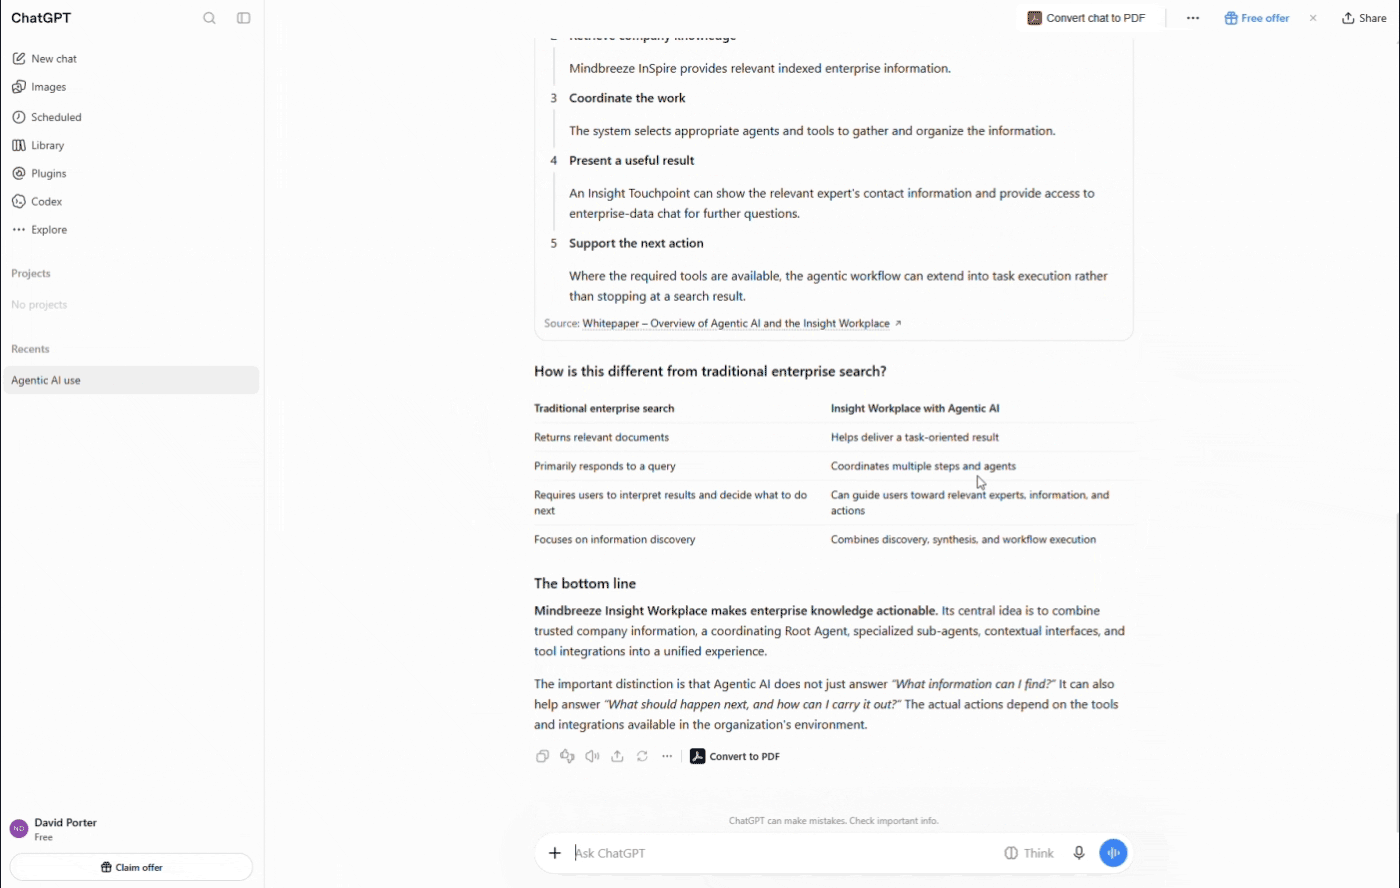
Mindbreeze InSpire is available as an agentic tool for customers that want to utilize the raw power of AI without compromising on security and transparency. Whether for in-house applications or intensive work in commercial AI platforms, integrating Mindbreeze InSpire API Tools via Model Context Protocol (MCP) drastically enhances the capabilities of your AI Assistants and Agents and opens up brand new use cases.
Due to ongoing developments and optimizations, the Mindbreeze InSpire 26.7 Release offers new features and improvements that increase security, quality and usability while administrators benefit from new monitoring features. Integrating Mindbreeze InSpire into commercial AI platforms, like OpenAI ChatGPT, Anthropic Claude or Microsoft Copilot, is now simpler designed. By providing a Server URL, the integration process is completed within a few clicks while agent-oriented authorization ensures a high level of security during the use of Mindbreeze InSpire as an agentic tool.
With the increased support of the industry standard OpenAI API and the end-to-end instrumentation, more options for monitoring and tracking LLMs and RAG pipelines are available. Administrators now receive more in-depth information about LLMs, RAG pipelines and processed requests in app.telemetry to enable more thorough problem analysis and detailed traceability.
For internal resource management and accounting purposes, administrators have the possibility to also track the LLM usage on the user and organization level. With this tracking configured, enterprises can monitor the internal usage of their LLMs in detail, and reallocate resources according to the usage and increase resource effectiveness.
Mindbreeze Insight Workplace – New features and optimizations
The Mindbreeze Insight Workplace is further enhanced with new features and optimizations that improve the user’s interaction with the PDF Preview and give administrators more options to adjust the Insight Workplace according to their requirements. Search queries can now be automatically forwarded to the keyword search of the PDF Preview to enable a smooth transition between search results and the PDF Preview. With the streaming of large PDFs optimized, users now seamlessly continue their research in the PDF Preview, refine the search query with query language, like “AND” or “OR”, and quickly access relevant text passages from particularly large PDF documents.
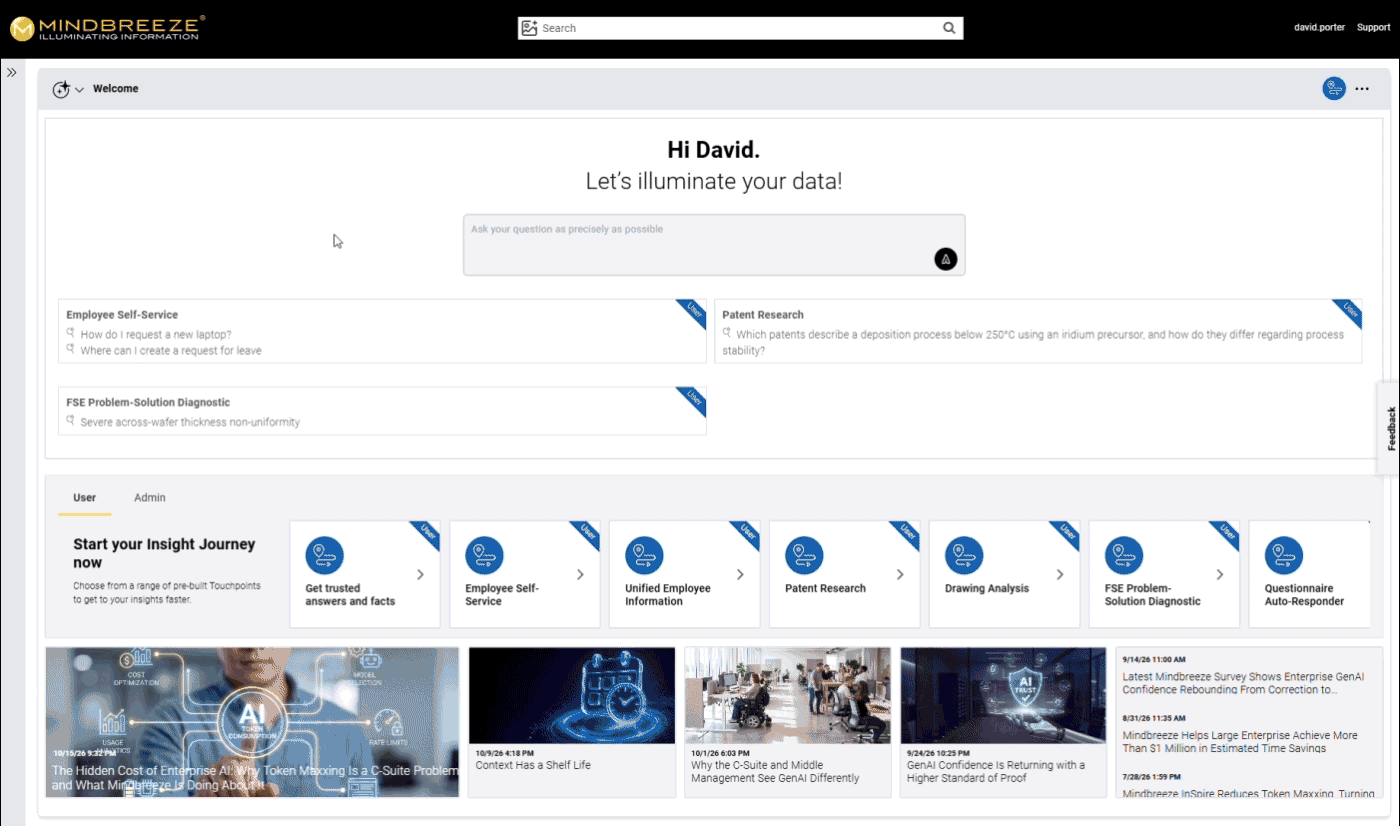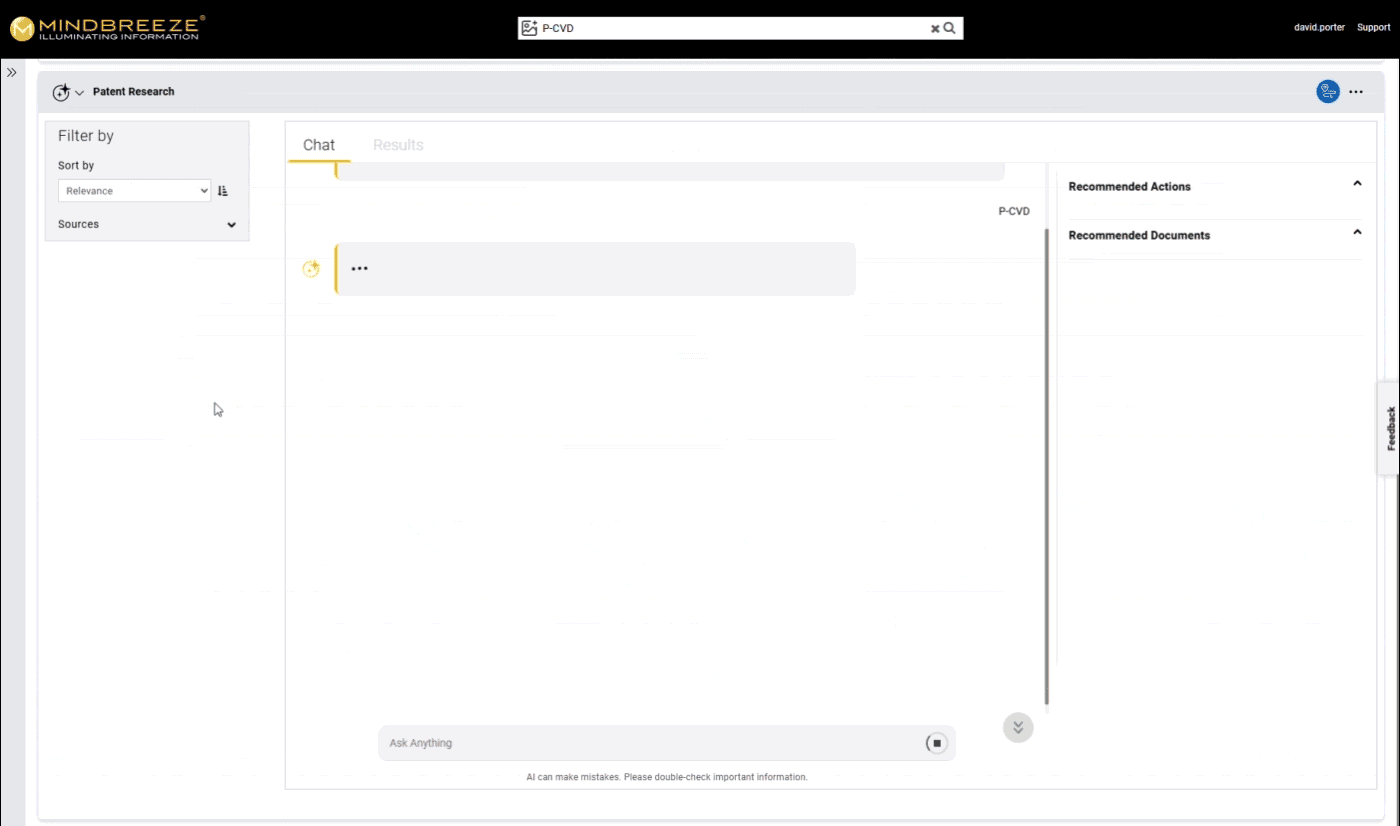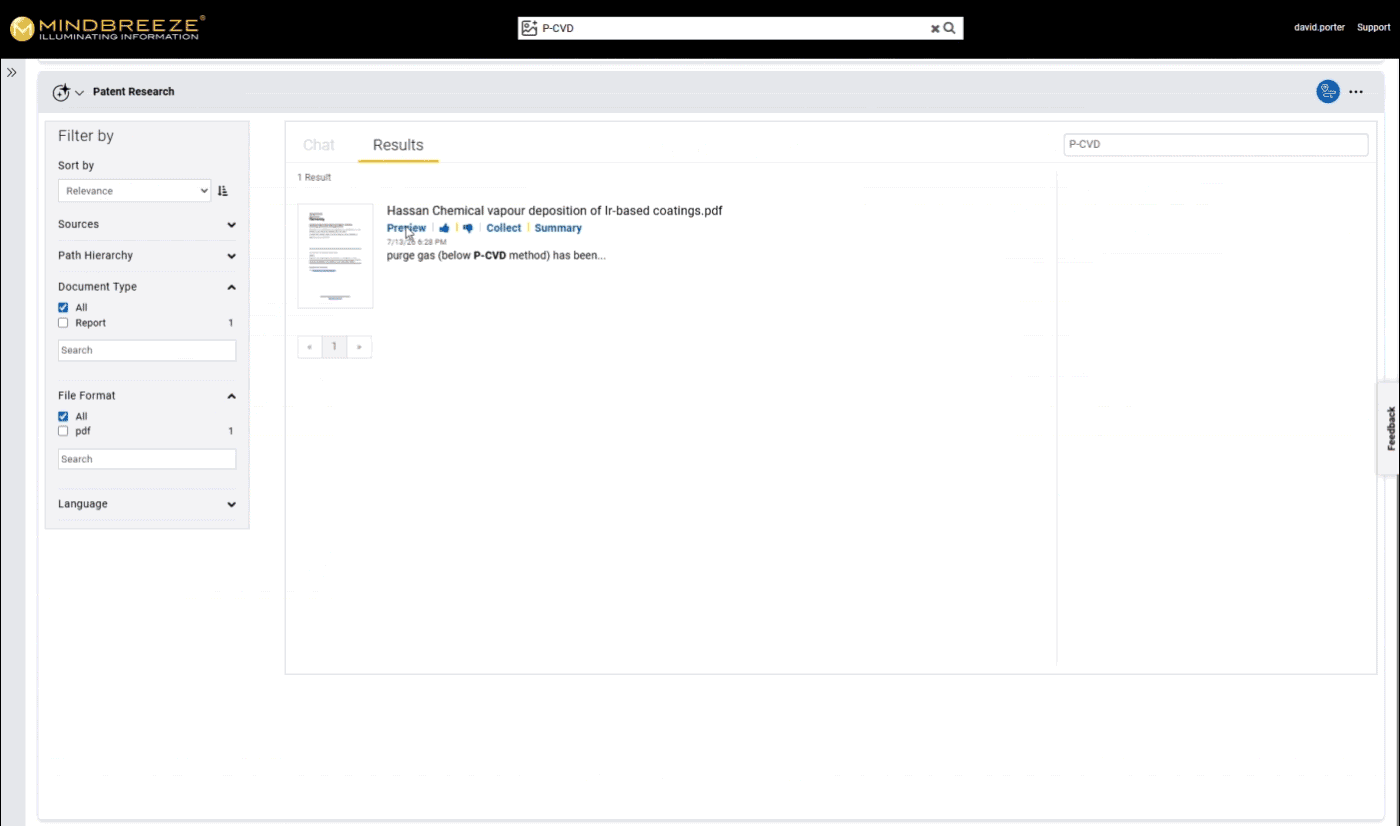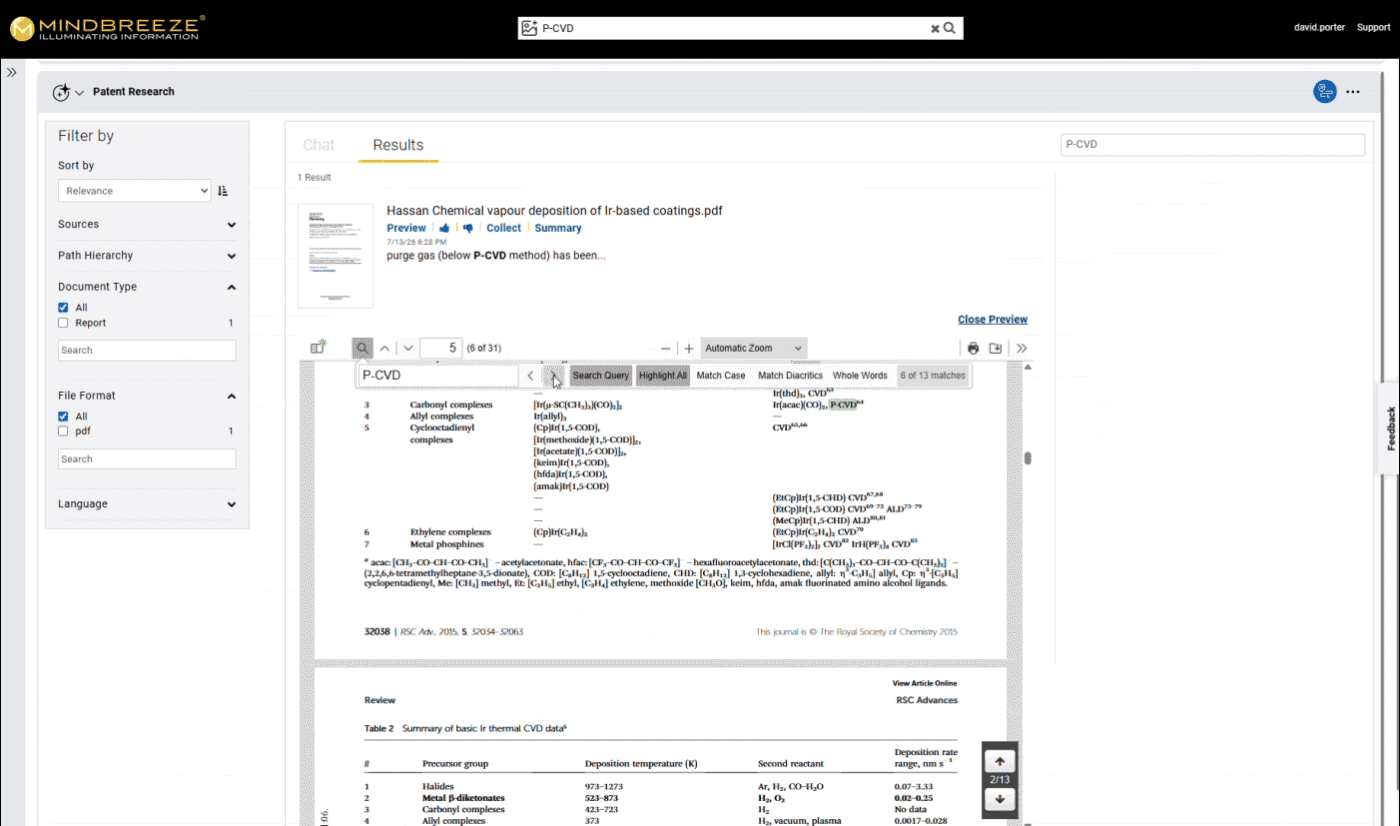
Administrators now also have the option to adjust the positioning of the PDF Preview by defining a custom position in the Mindbreeze Insight Touchpoint. When switching between pages of search results, a scrolling action can be configured which, for example, automatically scrolls to the top of the next page, to improve navigation. In addition, the loading of content in the first Insight Touchpoint has been optimized and it is possible to hide the area where the name of the Insight Touchpoint is displayed.
For Insight Workplace configurations where only the results of the currently active Insight Touchpoint are displayed, administrators can improve the performance of the Insight Workplace by focusing the Agentic AI on generating new content.
New, Extended and Updated
Connection of Data Sources & Indexing
Connector for GraphQL – Increased capabilities for content extraction
The Mindbreeze InSpire 26.7 Release increases the capabilities of the Connector for GraphQL to offer more support for administrators who handle complex cases of content extraction. With the newly added support of JSONPaths, nested JSON structures and scattered content can be navigated more easily, while the query language can be used to precisely define the content that is to be extracted by the new JSONFilter. This gives administrators the possibility to configure the content extraction in more detail while keeping the configuration process compact and easy.
ServiceNow Connector – More flexible configuration of Access Control Lists
More flexibility was added to the configuration of Access Control Lists (ACLs) in the ServiceNow Connector. Administrators are now able to configure ACLs more closely according to their requirements and use cases to increase the efficiency of the processing of ACLs. For use cases where documents have no ACLs, the processing can be disabled and “Default-ACLs” can be assigned, which results in a performance increase of the connector.
Applications
Enhanced handling of WordPerfect and JSON documents
Mindbreeze InSpire users that work with WordPerfect and JSON documents receive more support with the Mindbreeze InSpire 26.7 Release. Documents that use the WordPerfect file format, like archive data, can now be transformed to PDF documents, which unlocks several PDF-compatible features like the PDF preview and text highlighting. This enables users to intuitively interact with information from WordPerfect documents in a modern and efficient way.
For JSON documents, a new JSON filter plugin is available that allows content extraction from JSON objects. Administrators can use the JSON filter plugin with, for example, the Connector for GraphQL, to represent content from JSON documents.
Security
Various updates
The Mindbreeze InSpire 26.7 Release includes various security updates for Chromium, Core OS, C++ Dependencies, Dell Firmware, Java, Keycloak, Kubectl and Python dependencies.
Additional Features
Simplified sharing of Mindbreeze Insight Workplace configuration files
The sharing of Insight Workplace configuration files between Mindbreeze InSpire instances is now easier and more intuitive. After the download of the configuration as a .tar folder, the entire folder can be uploaded and immediately applied to another Mindbreeze InSpire instance. This allows administrators to flexibly share Insight Workplace configurations and, for example, significantly speed up the entire initial configuration process of the Insight Workplace by uploading a pre-defined “default configuration.”
Existing Insight Workplace configurations can be quickly and easily updated by uploading the latest Insight Workplace configuration files. The previous configuration is preserved in a backup file, making it easy to incorporate custom changes and modifications into the updated Insight Workplace configuration. Administrators are therefore able to equip their Insight Workplace configurations with the latest features and improvements while retaining custom changes and modifications.
Changelog
- Updated: CoreOS to version 44.20260913.3.2 (CVE-2026-5704,CVE-2026-59999,CVE-2026-59995,CVE-2026-14456,CVE-2026-53783,CVE-2026-53789,CVE-2026-53784,CVE-2026-53801,CVE-2026-53797,CVE-2026-53798,CVE-2026-53795,CVE-2026-53803,CVE-2026-53800,CVE-2026-53796,CVE-2026-53785,CVE-2026-53802,CVE-2026-53791,CVE-2026-53786,CVE-2026-70461,CVE-2026-53792,CVE-2026-70458,CVE-2026-70462,CVE-2026-70460,CVE-2026-53788,CVE-2026-53799,CVE-2026-53793,CVE-2026-70455,CVE-2026-70463,CVE-2026-70456,CVE-2026-53790,CVE-2026-70452,CVE-2026-70457,CVE-2026-70464,CVE-2026-53794,CVE-2026-70459,CVE-2026-70454,CVE-2026-70453,CVE-2026-72693,FEDORA-2026-b4cd43a7dc,FEDORA-2026-3d9bd126ce,CVE-2026-80590,FEDORA-2026-51251b4657,CVE-2026-18798,FEDORA-2026-0d885c0533,FEDORA-2026-9ce2715225,CVE-2026-18477,CVE-2026-18508,CVE-2026-63383,CVE-2026-63382,CVE-2026-63379,CVE-2026-63381,CVE-2026-63387,CVE-2026-63388,CVE-2026-63384,CVE-2026-63385,CVE-2026-13608,CVE-2026-18924,CVE-2026-19931,CVE-2026-80229,CVE-2026-80230,CVE-2026-80231,CVE-2026-80255,CVE-2026-82208,CVE-2026-82209,CVE-2026-80256,CVE-2026-54874,CVE-2026-14457,CVE-2026-63072,CVE-2026-63073,CVE-2026-63074,CVE-2026-63075,CVE-2026-63076,CVE-2026-75803,CVE-2026-89085,CVE-2026-89088,FEDORA-2026-ca91e91bf0,CVE-2026-80844,CVE-2026-81000,CVE-2026-68121,CVE-2026-74469,CVE-2026-84782,CVE-2026-35189,CVE-2026-35191,CVE-2026-42772,CVE-2026-54872,CVE-2026-54873,CVE-2026-54875,CVE-2026-72897,CVE-2026-75804,CVE-2026-75805,CVE-2026-75806,CVE-2026-77696,CVE-2026-84784,CVE-2026-47587,CVE-2026-47567,CVE-2026-47566,CVE-2026-47596,CVE-2026-47601,CVE-2026-47518,CVE-2026-47595,CVE-2026-47564,CVE-2026-47491,CVE-2026-47489,CVE-2026-47516,CVE-2026-47572,CVE-2026-47569,CVE-2026-47560,CVE-2026-47501,CVE-2026-47563,CVE-2026-47561,CVE-2026-47559,CVE-2026-47558,CVE-2026-47556,CVE-2026-47553,CVE-2026-47552,CVE-2026-47551,CVE-2026-47548,CVE-2026-47545,CVE-2026-47540,CVE-2026-47530,CVE-2026-47528,CVE-2026-47523,CVE-2026-47514,CVE-2026-47513,CVE-2026-47512,CVE-2026-47511,CVE-2026-47510,CVE-2026-47508,CVE-2026-47507,CVE-2026-47500,CVE-2026-47494,CVE-2026-47600,CVE-2026-47599,CVE-2026-47597,CVE-2026-47588,CVE-2026-47594,CVE-2026-47592,CVE-2026-47591,CVE-2026-47590,CVE-2026-47589,CVE-2026-47554,CVE-2026-47602,CVE-2026-47598,CVE-2026-47533,CVE-2026-47538,CVE-2026-47547,CVE-2026-47546,CVE-2026-47543,CVE-2026-47542,CVE-2026-47537,CVE-2026-47529,CVE-2026-47527,CVE-2026-47525,CVE-2026-47524,CVE-2026-47515,CVE-2026-47509,CVE-2026-47532,CVE-2026-47522,CVE-2026-47586,CVE-2026-47565,CVE-2026-47534,CVE-2026-47557,CVE-2026-47555,CVE-2026-47517,CVE-2026-47492,CVE-2026-47603,CVE-2026-47604,CVE-2026-47568,CVE-2026-47526,CVE-2026-47531,CVE-2026-47562,CVE-2026-47502,CVE-2026-47504).
- Updated: Dell Firmware (CVE-2026-20712, CVE-2026-6726, CVE-2026-6727, CVE-2026-20707, CVE-2026-20917, CVE-2026-20705, CVE-2026-20713, CVE-2026-20775, CVE-2026-20885, CVE-2026-20898, CVE-2026-20901, DSA-2026-415).
- Updated: Python dependency (CVE-2026-101917, CVE-2026-101918, CVE-2026-102265, CVE-2026-102266, CVE-2026-102267, CVE-2026-102268, CVE-2026-102269, CVE-2026-102270, CVE-2026-102271, CVE-2026-102272, CVE-2026-102273, CVE-2026-102274, CVE-2026-102275, CVE-2026-102993, CVE-2026-102994, CVE-2026-102995, CVE-2026-102996, CVE-2026-102997, CVE-2026-102998, CVE-2026-102999, CVE-2026-103000, CVE-2026-103001, CVE-2026-104873, CVE-2026-104874, CVE-2026-13346, CVE-2026-49264, CVE-2026-49265, CVE-2026-59951, CVE-2026-69112, CVE-2026-97687, CVE-2026-97688, CVE-2026-97689).
- Updated: kubectl to version 1.37 (CVE-2025-68121, CVE-2025-61729, CVE-2025-61725, CVE-2025-61724, CVE-2025-58188, CVE-2025-58186, CVE-2025-47912).
- Updated: Keycloak to version 26.7.3 (CVE-2026-4874, CVE-2026-37977, CVE-2026-42581, CVE-2026-3009, CVE-2026-2092, CVE-2026-3872, CVE-2026-4366, CVE-2026-3190, CVE-2026-3911, CVE-2026-42584, CVE-2026-42587, CVE-2026-41417, CVE-2026-42580, CVE-2026-42581, CVE-2026-42585, CVE-2026-42578, CVE-2026-45292, CVE-2026-39852, CVE-2026-6860, CVE-2026-5588, CVE-2026-7307, CVE-2026-7504, CVE-2026-7507, CVE-2026-7571, CVE-2026-37978, CVE-2026-37979, CVE-2026-37980, CVE-2026-37982, CVE-2026-7500, CVE-2026-8830, CVE-2026-8922, CVE-2026-37977, CVE-2026-44893, CVE-2026-48059, CVE-2026-50020, CVE-2026-47244, CVE-2026-48043, CVE-2026-50560, CVE-2026-44249, CVE-2026-45416, CVE-2026-50010, CVE-2026-45674, CVE-2026-47691, CVE-2026-45673, CVE-2026-45536).
- Updated: pcre2 to version 10.48 (CVE-2026-89156, CVE-2026-89161, CVE-2026-89160, CVE-2026-89158, CVE-2026-89157).
- Updated: Expat to version 2.8.4 and 2.8.5 (CVE-2026-66046, CVE-2026-76956, CVE-2026-76641, CVE-2026-76957, CVE-2026-93990).
- Updated: Tomcat to version 9.0.122 (CVE-2026-73180 CVE-2026-68763 CVE-2026-68569 CVE-2026-68525 CVE-2026-66422 CVE-2026-65927 CVE-2026-65905 CVE-2026-65637 CVE-2026-65183 CVE-2026-65182 CVE-2026-86247 CVE-2026-86246 CVE-2026-86243 CVE-2026-87022 CVE-2026-86350 CVE-2026-86248 CVE-2026-79677 CVE-2026-78437 CVE-2026-78383 CVE-2026-77791 CVE-2026-77762 CVE-2026-77756 CVE-2026-76183 CVE-2026-75973 CVE-2026-73581).
- Updated: Chromium to version 154.0.8037.92 (CVE-2026-76017,CVE-2026-76018,CVE-2026-76019,CVE-2026-76020,CVE-2026-76021,CVE-2026-76022,CVE-2026-76023,CVE-2026-79282,CVE-2026-79290,CVE-2026-79054,CVE-2026-79121,CVE-2026-79224,CVE-2026-79052,CVE-2026-79150,CVE-2026-78935,CVE-2026-79012,CVE-2026-79200,CVE-2026-78989,CVE-2026-79069,CVE-2026-79175,CVE-2026-79218,CVE-2026-79195,CVE-2026-78939,CVE-2026-79194,CVE-2026-79247,CVE-2026-79219,CVE-2026-79047,CVE-2026-79292,CVE-2026-78986,CVE-2026-79039,CVE-2026-78934,CVE-2026-79011,CVE-2026-78911,CVE-2026-79257,CVE-2026-79202,CVE-2026-79212,CVE-2026-79183,CVE-2026-79155,CVE-2026-79093,CVE-2026-79019,CVE-2026-79187,CVE-2026-79288,CVE-2026-79130,CVE-2026-78965,CVE-2026-79117,CVE-2026-79082,CVE-2026-79111,CVE-2026-79072,CVE-2026-79142,CVE-2026-78948,CVE-2026-78908,CVE-2026-78895,CVE-2026-79043,CVE-2026-79235,CVE-2026-79232,CVE-2026-79118,CVE-2026-79174,CVE-2026-78900,CVE-2026-79188,CVE-2026-79189,CVE-2026-79048,CVE-2026-79240,CVE-2026-79014,CVE-2026-79198,CVE-2026-79131,CVE-2026-79149,CVE-2026-79275,CVE-2026-79138,CVE-2026-79026,CVE-2026-79027,CVE-2026-78904,CVE-2026-78899,CVE-2026-78954,CVE-2026-79274,CVE-2026-78938,CVE-2026-78952,CVE-2026-79236,CVE-2026-79078,CVE-2026-84353,CVE-2026-84352,CVE-2026-84354,CVE-2026-84359,CVE-2026-84357,CVE-2026-84324,CVE-2026-84349,CVE-2026-84326,CVE-2026-84333,CVE-2026-84351,CVE-2026-84325,CVE-2026-87464,CVE-2026-87488,CVE-2026-87438,CVE-2026-87527,CVE-2026-87628,CVE-2026-87512,CVE-2026-87585,CVE-2026-87444,CVE-2026-87447,CVE-2026-87440,CVE-2026-87633,CVE-2026-87525,CVE-2026-87578,CVE-2026-87517,CVE-2026-87524,CVE-2026-87569,CVE-2026-87554,CVE-2026-87467,CVE-2026-87492,CVE-2026-87520,CVE-2026-87514,CVE-2026-87650,CVE-2026-87596,CVE-2026-87654,CVE-2026-87604,CVE-2026-87621,CVE-2026-87647,CVE-2026-87646,CVE-2026-87500,CVE-2026-87572,CVE-2026-87460,CVE-2026-87542,CVE-2026-87639,CVE-2026-87552,CVE-2026-87651,CVE-2026-87587,CVE-2026-87564,CVE-2026-87498,CVE-2026-87499,CVE-2026-87607,CVE-2026-87558,CVE-2026-87581,CVE-2026-87480,CVE-2026-87612,CVE-2026-87536,CVE-2026-87474,CVE-2026-87504,CVE-2026-87640,CVE-2026-87491,CVE-2026-87478,CVE-2026-87446,CVE-2026-87657,CVE-2026-87434,CVE-2026-87487,CVE-2026-87453,CVE-2026-87588,CVE-2026-87636,CVE-2026-87611,CVE-2026-87606,CVE-2026-87456,CVE-2026-87553,CVE-2026-87658,CVE-2026-87465,CVE-2026-87515,CVE-2026-87547,CVE-2026-87442,CVE-2026-87506,CVE-2026-87433,CVE-2026-87557,CVE-2026-87457,CVE-2026-87503,CVE-2026-87481,CVE-2026-87537,CVE-2026-87471,CVE-2026-87485,CVE-2026-87652,CVE-2026-87582,CVE-2026-87466,CVE-2026-87603,CVE-2026-87615,CVE-2026-87642,CVE-2026-87577,CVE-2026-87449,CVE-2026-87613,CVE-2026-87645,CVE-2026-87443,CVE-2026-87630,CVE-2026-87590,CVE-2026-87580,CVE-2026-87482,CVE-2026-87497,CVE-2026-87579,CVE-2026-87576,CVE-2026-87476,CVE-2026-87475,CVE-2026-87436,CVE-2026-87479,CVE-2026-87513,CVE-2026-87432,CVE-2026-87560,CVE-2026-87521,CVE-2026-87539,CVE-2026-87648,CVE-2026-87534,CVE-2026-87562,CVE-2026-87556,CVE-2026-87508,CVE-2026-87643,CVE-2026-87573,CVE-2026-87548,CVE-2026-87501,CVE-2026-87452,CVE-2026-87516,CVE-2026-87599,CVE-2026-87507,CVE-2026-87559,CVE-2026-87472,CVE-2026-87486,CVE-2026-87655,CVE-2026-87462,CVE-2026-87649,CVE-2026-87445,CVE-2026-87567,CVE-2026-87496,CVE-2026-87441,CVE-2026-87549,CVE-2026-87458,CVE-2026-87574,CVE-2026-87495,CVE-2026-87541,CVE-2026-87451,CVE-2026-87570,CVE-2026-87555,CVE-2026-87600,CVE-2026-87532,CVE-2026-87439,CVE-2026-87450,CVE-2026-87505,CVE-2026-87622,CVE-2026-87540,CVE-2026-87594,CVE-2026-87518,CVE-2026-87589,CVE-2026-87484,CVE-2026-87530,CVE-2026-87550,CVE-2026-87494,CVE-2026-87483,CVE-2026-87454,CVE-2026-87616,CVE-2026-87535,CVE-2026-87644,CVE-2026-87533,CVE-2026-87635,CVE-2026-87641,CVE-2026-87431,CVE-2026-87493,CVE-2026-87625,CVE-2026-87468,CVE-2026-87563,CVE-2026-87510,CVE-2026-87435,CVE-2026-87531,CVE-2026-87637,CVE-2026-87529,CVE-2026-87470,CVE-2026-87586,CVE-2026-87584,CVE-2026-87632,CVE-2026-87528,CVE-2026-87623,CVE-2026-87566,CVE-2026-87638,CVE-2026-87455,CVE-2026-87591,CVE-2026-87526,CVE-2026-87609,CVE-2026-87610,CVE-2026-87626,CVE-2026-87629,CVE-2026-87653,CVE-2026-87634,CVE-2026-87429,CVE-2026-87618,CVE-2026-87614,CVE-2026-87619,CVE-2026-87561,CVE-2026-87598,CVE-2026-87519,CVE-2026-87543,CVE-2026-87522,CVE-2026-87568,CVE-2026-87656,CVE-2026-87511,CVE-2026-87627,CVE-2026-87595,CVE-2026-87592,CVE-2026-87620,CVE-2026-87502,CVE-2026-87448,CVE-2026-87459,CVE-2026-87463,CVE-2026-87546,CVE-2026-87538,CVE-2026-87545,CVE-2026-87617,CVE-2026-87523,CVE-2026-87565,CVE-2026-87597,CVE-2026-87624,CVE-2026-87605,CVE-2026-87490,CVE-2026-87583,CVE-2026-87509,CVE-2026-87473,CVE-2026-87461,CVE-2026-87631,CVE-2026-87469,CVE-2026-87489,CVE-2026-87575,CVE-2026-87571,CVE-2026-87477,CVE-2026-87551,CVE-2026-87608,CVE-2026-87437,CVE-2026-87602,CVE-2026-87601,CVE-2026-87544,CVE-2026-87430,CVE-2026-87593,CVE-2026-85046,CVE-2026-85052,CVE-2026-85043,CVE-2026-85048,CVE-2026-85045,CVE-2026-85050,CVE-2026-85053,CVE-2026-85042,CVE-2026-85049,CVE-2026-85051,CVE-2026-85047,CVE-2026-85044,CVE-2026-95350,CVE-2026-95357,CVE-2026-95339,CVE-2026-95281,CVE-2026-95313,CVE-2026-95349,CVE-2026-95284,CVE-2026-95322,CVE-2026-95329,CVE-2026-95356,CVE-2026-95310,CVE-2026-95301,CVE-2026-95291,CVE-2026-95355,CVE-2026-95315,CVE-2026-95298,CVE-2026-95372,CVE-2026-95324,CVE-2026-95283,CVE-2026-95293,CVE-2026-95274,CVE-2026-95282,CVE-2026-95373,CVE-2026-95277,CVE-2026-95348,CVE-2026-95335,CVE-2026-95338,CVE-2026-95318,CVE-2026-95286,CVE-2026-95365,CVE-2026-95343,CVE-2026-95280,CVE-2026-95304,CVE-2026-95306,CVE-2026-95299,CVE-2026-95351,CVE-2026-95287,CVE-2026-95366,CVE-2026-95382,CVE-2026-95381,CVE-2026-95331,CVE-2026-95297,CVE-2026-95375,CVE-2026-95302,CVE-2026-95362,CVE-2026-95369,CVE-2026-95376,CVE-2026-95359,CVE-2026-95294,CVE-2026-95337,CVE-2026-95346,CVE-2026-95320,CVE-2026-95317,CVE-2026-95345,CVE-2026-95330,CVE-2026-95370,CVE-2026-95303,CVE-2026-95360,CVE-2026-95295,CVE-2026-95276,CVE-2026-95314,CVE-2026-95371,CVE-2026-95353,CVE-2026-95363,CVE-2026-95341,CVE-2026-95354,CVE-2026-95384,CVE-2026-95336,CVE-2026-95290,CVE-2026-95325,CVE-2026-95275,CVE-2026-95374,CVE-2026-95300,CVE-2026-95321,CVE-2026-95323,CVE-2026-95332,CVE-2026-95312,CVE-2026-95344,CVE-2026-95289,CVE-2026-95347,CVE-2026-95311,CVE-2026-95358,CVE-2026-95333,CVE-2026-95307,CVE-2026-95285,CVE-2026-95278,CVE-2026-95327,CVE-2026-95334,CVE-2026-95308,CVE-2026-95292,CVE-2026-95352,CVE-2026-95279,CVE-2026-95367,CVE-2026-95385,CVE-2026-95368,CVE-2026-95319,CVE-2026-95326,CVE-2026-95309,CVE-2026-95361,CVE-2026-95288,CVE-2026-95380,CVE-2026-95342,CVE-2026-95296,CVE-2026-95316,CVE-2026-95328,CVE-2026-95340,CVE-2026-95364,CVE-2026-95305,CVE-2026-93374,CVE-2026-93372,CVE-2026-93375,CVE-2026-93382,CVE-2026-93387,CVE-2026-93373,CVE-2026-93381,CVE-2026-93379,CVE-2026-93377,CVE-2026-93380,CVE-2026-93384,CVE-2026-93383,CVE-2026-93376,CVE-2026-93378,CVE-2026-93385,CVE-2026-93386,CVE-2026-102331,CVE-2026-102317,CVE-2026-102312,CVE-2026-102313,CVE-2026-102299,CVE-2026-102306,CVE-2026-102307,CVE-2026-102323,CVE-2026-102303,CVE-2026-102311,CVE-2026-102300,CVE-2026-102326,CVE-2026-102316,CVE-2026-102304,CVE-2026-102328,CVE-2026-102309,CVE-2026-102325,CVE-2026-102308,CVE-2026-102301,CVE-2026-102319,CVE-2026-102324,CVE-2026-102318,CVE-2026-102329,CVE-2026-102315,CVE-2026-102302,CVE-2026-102321).
- Fix for: eMudhra CA certificates are compromised (GHSA-6q48-6c7w-9gw2, CVE-2026-114406, CVE-2026-91403).
- Fix for: No cookies for app.telemetry requests (GHSA-6q48-6c7w-9gw2, CVE-2026-114406, CVE-2026-91403).
- Updated: Dotnet to version 10.0.
- Added: Structured logging in Kubernetes.
- Added: Support for JSONPath, i18n title and nested pivoting as well as a new JSON content filter into the Connector for GraphQL.
- Added: Directory upload through the SDK File Manager.
- Added: Support for default redirect from legacy client to the Insight Workplace.
- Added: The widget "pages" now supports the attribute “data-scroll-selector” to automatically scroll to a specific element after navigating to another page.
- Added: Inline PDF preview can be opened at a custom position on the Insight Touchpoint via result enrichments (preview_target_selector, exclusive, etc.).
- Added: The header of the Insight Touchpoint can be shown or hidden via the themeDescriptor setting “apps.workplace.showHeader”.
- Added: A new config option (skipGenerationIfOnlyOneAppAvailable) enables the skipping of the AI generation when only one Insight Touchpoint is displayed.
- Added: The ability to set the default java version for all java services via an environment variable.
- Added: Support for plugin URL that are parameterized with “category” and “categoryinstance”.
- Added: Support for “orderby” in the React library.
- Added: Support for the WordPerfect file format in the Filter Service “FilterPlugin.OfficeDocumentToPDFContentFilter”.
- Added: Optional updates for built-in Tika filters.
- Added: The MCP Authentication Proxy uses Microsoft Entra ID as Identity Provider.
- Added: The Consent Page for MCP connection can be configured and customized.
- Fix for: The column "Effective Search Request" in app.telemetry was truncated.
- Fix for: Accessibility style and container for Autocomplete feature.
- Fix for: API requests of builtin API Tools are now sent as protobuf binary.
- Fix for: Item events were not deleted by SharePoint, if they were combined with role changes in the list permissions.
- Fix for: The actions “Vote up” and “Vote down” were not rendered in some circumstances.
- Fix for: An icon was missing on the first action button due to a CSS rule that hid it before the content for the first list item was loaded.
- Fix for: References via property expressions to storage-only properties only resolved one value, even if multiple references with a value were found.
- Fix for: api.v2.search did not return default properties, when no properties were requested.
- Fix for: Development Snapshots did not include apps referenced in “Additional context” with paths that were more than two levels.
- Fix for: The retrieved item limit did not work properly in AI Answers.
- Fix for: The Bootloader Update Service failed after the update.
- Fix for: In the Web Connector, end-of-crawl reported errors when requests timed out, even when they were successfully retried later.
- Fix for: The recent queries in the autocomplete feature could not be removed.
- Fix for: When using JWT Authentication, API with expired access token returned the error code 403 but should have returned the error code 401 and the WWW-Authenticate header was missing.
- Improved: PDF preview now supports search terms inside PDFs using the Mindbreeze Query Language.
- Changed: If the persistence mode is not set, the default persistence mode “implicit” is automatically used in the Insight Workplace.